
If an application requires that greater than oneCSP perform operations utilizing the identical private key, then thatkey have to be exported from some source and imported to allCSPs needing to use it. Wrapping keys as key blobs managesthe downside of different key formats amongst different CSPs.This assumes that the key length is suitable to all CSPsusing the same key. The nature of the cryptographic functions contained in anyparticular CSP is dependent upon what task the CSP was designed toperform. For instance, a VISA cryptographic hardware tokenwould be in a position to digitally sign bank card transactions onbehalf of the card’s owner.
Ten Things Executives Need To Find Out About Quantum Safety
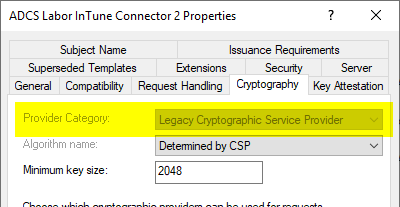
The Cryptographic Supplier contains a wide range of cryptographic algorithms that meet trade standards, similar to Advanced Encryption Normal (AES), Digital Signature Algorithm (DSA), and Elliptic Curve Cryptography (ECC). This ensures compatibility with a broad range of applications and techniques. Since there are so much of completely different providers, it’s best to divide into teams based on throughout capabilities in every use case.
Background: Csp Vs Ksp
Use this information to transform the Cryptographic Service Provider (CSP) of third-party certificates to a SHA 2-enabled CSP through the PFX Convert Script to support SAML functions that require SHA 2 assertions. out Buffer to be filled by the operate with the computed cryptogram. in, out Buffer to be crammed by the operate with the computed message. Watch this webinar to learn to prepare for the post-quantum era with hardware security modules.

Which Cryptographic Service Supplier Ought To I Use?
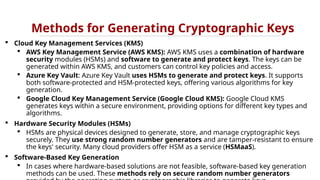
Within MSCAPI (and therefore SafeNet ProtectToolkit-M), key pairs are held inside a key container, which is stored inside a keyset. Automatically assess cryptographic danger posture, enforce coverage, and secure keys, secrets, and certificates throughout distributed functions, divisions, and groups. The Entrust Cryptographic Security Platform unifies PKI, HSMs, certificates lifecycle administration, and key & secrets and techniques administration in a cryptographic trust layer for centralized visibility, governance, and automation. The CSMM API defines how personal keys might be passed up and down via the layers of the CDSA, nevertheless it doesn’t specify how private keys shall be stored inside the CSP. Security-conscious functions use these high-level ideas to provide authentication, information integrity, information and communication privateness, and nonrepudiation of messages to the end-users. The CSMM API defines how personal keys will be passed up anddown through the layers of the CDSA, nevertheless it doesn’t specifyhow non-public keys will be stored inside the CSP.
Embracing legacy CSPs, the CSSM structure defines an optionally available adaptation layer between the Cryptographic Providers Module Manager and a CSP. New CSPs might support the CSSM SPI immediately (without assistance from an adaptation layer). Software CSPs could be carried as an executable file on frequent forms of detachable media. The elements that implement a CSP have to be digitally signed, to authenticate their origin and integrity. This requirement extends to composite implementations involving both https://www.sacramento-marketing.com/category/technology/ software and hardware.
The CSP is accountable forcontrolling entry to the private keys it secures. Most CSPs arecapable of importing non-public keys created by other CSPs andproviding secured storage for such keys. The first CryptoAPI function referred to as by an software that makes use of any cryptographic APIs is the GetCryptoProvider function.
- Apart from this, there are two keysets required by the SafeNet ProtectToolkit-M system for its inside processes.
- When an application calls GetCryptoProvider to obtain a CSP deal with, it specifies a provider type and, optionally, a provider name.
- Cryptographic Service Providers (CSPs) retailer, access and create cryptographic keys– the constructing blocks of PKI.
- Our new international examine with Ponemon Institute goals to add clarity to your cryptographic security methods.
Turn certificates chaos into confidence with centralized visibility, automation, and lifecycle management for enterprise certificates. Defend unstructured information with agentless file encryption and centralized key management across distributed methods. Improve to Microsoft Edge to take advantage of the newest features, security updates, and technical support. Computes a symmetric key cryptography authenticator in response to a problem generated by the consumer utility. For hardware solutions such as Smart Cards and Hardware Security Modules (HSMs), third get together software is typically needed for optimal performance. Newer Subsequent Gen KSPs and more commonplace Microsoft CSPs are listed under for a comparison.